
Your patients' records, protected at every layer
Your desk sees what the desk needs, you see what you need, and patients decide what they share. Everything sensitive is logged, and the platform is security audited.
In short
- 01Staff see only what their role allows
- 02Patients control what they share
- 03Security audited and ABDM compliant
How your clinic's data is protected, layer by layer
Every safeguard between the outside world and your patients' records. Scroll to arm them, one at a time.
- Layer 01
Your clinic's records stay separate
Each clinic and hospital on MedChaaya has its own records, kept apart from everyone else's.
- Separate per clinic
- No cross-clinic browsing
- Layer 02
Role-based staff access
Your receptionist or nurse gets front-desk permissions only. You can deactivate a login at any time.
- Front-desk permission group
- Activate and deactivate staff
- Layer 03
The desk does not read clinical documents
At the front desk, clinical documents show only their title and date.
- Contents stay with the doctor
- Layer 04
Patients control their own documents
Documents a patient holds in their own app need their permission. Patients see which doctors can access their record, until when, and can withdraw it.
- Access requests
- Time-limited access after a visit
- Layer 05
ABDM with consent
Records from other providers arrive only after the patient consents in their ABHA app, and they arrive encrypted.
- ABDM Milestones 1 to 3
- FHIR R4 exchange
- Layer 06
Private video calls
Audio and video travel directly between you and the patient and are not recorded by MedChaaya.
- Peer-to-peer calls
- Layer 07
AI that never decides
AI is optional, every output carries a disclaimer, and nothing it produces is applied without your review.
- Switched on per account
- Marked as AI
- Layer 08
An audit log
Sensitive actions are logged, and patients can read the log of who viewed their record.
- Who did what, and when
- Layer 09
An audited platform
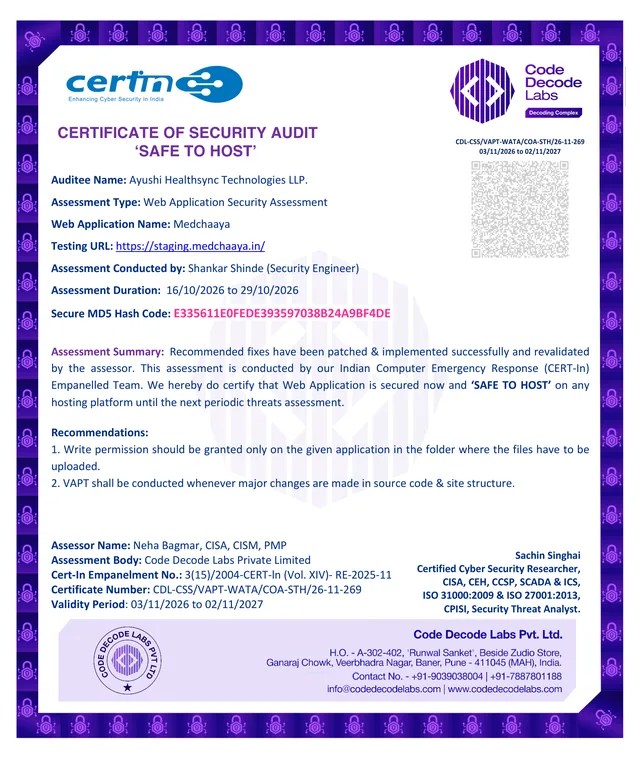
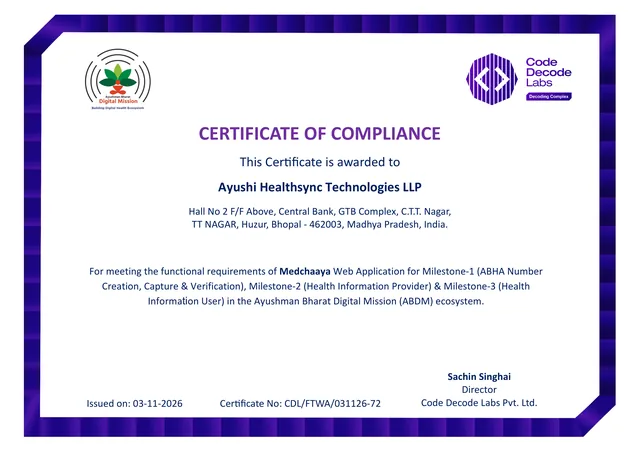
MedChaaya holds a security audit certificate (Safe to Host) and ABDM compliance, and its privacy policy is aligned to the DPDP Act, 2023.
- Security audit: Safe to Host
- Privacy policy aligned to the DPDP Act, 2023
Common questions
Is my medical data safe, and who can see it?
Patients choose what to share and can revoke access. Staff and doctors see only what their role, hospital and permissions allow, each hospital's records are kept separate, and an audit log records who did what. With an on-premise deployment, patient records are stored on your own infrastructure.
Is MedChaaya security audited and ABDM compliant?
Yes. Code Decode Labs, a CERT-In empanelled auditor, ran a web application security assessment of MedChaaya in October 2026; every fix was re-validated and MedChaaya was certified Safe to Host until 2 November 2027. MedChaaya also holds a certificate of compliance for ABDM Milestones 1, 2 and 3 (ABHA creation and verification, Health Information Provider and Health Information User). Both certificates are on the certifications page.
Can I get a patient's records from other hospitals?
Yes, through ABDM. Send a consent request by the patient's ABHA address, record type and date range. The patient approves it in their ABHA app, and the records arrive encrypted and are shown as structured views.
Open your clinic on MedChaaya
Register as a doctor, set up your clinic in one click, and start seeing patients.
Start your clinic